Most attacks are not aimed at you in particular. They are automated, opportunistic and pointed at whatever is exposed: an unpatched VPN, a reused password, a staff member who answers a text message. That is why cybersecurity matters to a small business as much as to a bank.
As a business owner, you should have a pragmatic security program and no longer rely on simple solutions like your antivirus or firewall to protect your company, employees, and customers’ data.
This guide gives nine reasons it matters, using the 2026 editions of IBM’s Cost of a Data Breach report and Verizon’s Data Breach Investigations Report (DBIR), plus the FBI’s 2025 Internet Crime Report. It ends with a short self-check you can run on systems you own.
Key takeaways
- The global average data breach cost $4.99 million in IBM’s 2026 report, a record and 12% higher than last year. In the US it was $11.5 million.
- Exploiting software vulnerabilities is now the most common way in (31% of breaches), ahead of stolen credentials (13%). It is the first time in the DBIR’s 19 years that credentials have not been first.
- Ransomware appeared in 48% of breaches, and 69% of those victims did not pay.
- Third parties were involved in 48% of breaches, up 60% year-on-year.
- The human element was involved in 62% of breaches.
- Antivirus and a firewall do not cover most of these routes. Patching, MFA, tested backups and vendor control do.
What Cybersecurity means for a business
Cybersecurity is the set of practices and tools that keep your systems, networks, and data confidential, available and unaltered.
For a business that translates into three practical goals: keep operating, keep customer and company data private, and be able to prove to customers, insurers, and regulators that you took reasonable care.
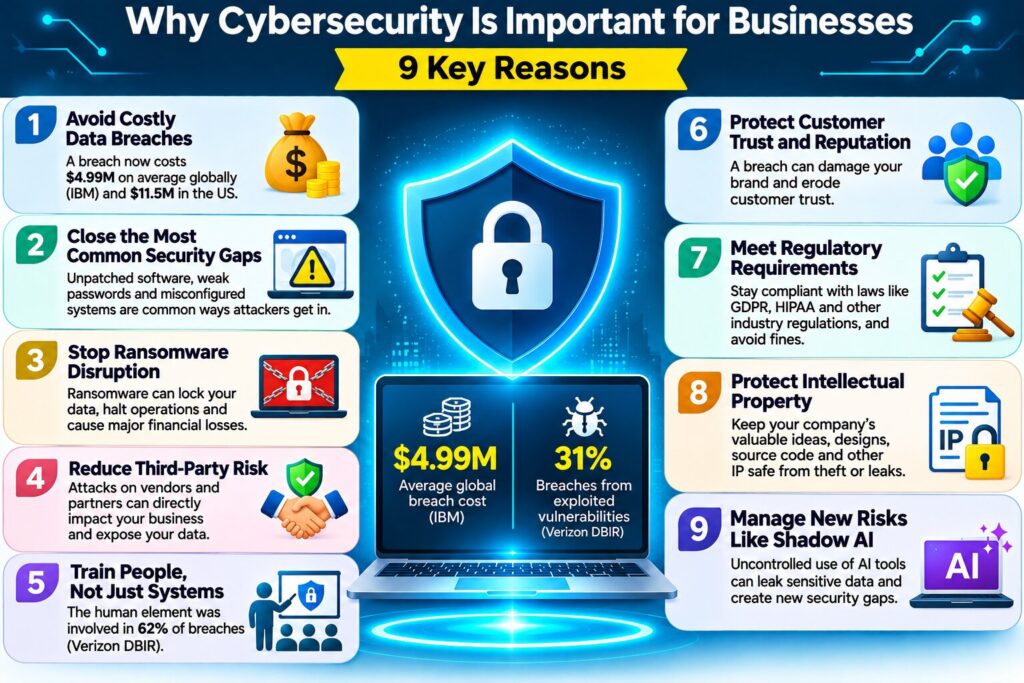
1. A breach costs more every year
IBM’s 2026 report puts the global average breach at $4.99 million, up 12% and a record, with the rise attributed to higher detection, escalation and lost-business costs (IBM, eSecurity Planet). The US average was $11.5 million.
Organizations took 247 days on average to identify and contain a breach, which reversed several years of gradual improvement. The 2025 edition had reported the first decline in five years ($4.44 million), so last year’s relief did not last.
Crime reports point the same way. The FBI’s 2025 Internet Crime Report counted more than one million complaints and roughly $21 billion in reported losses, up from $16.6 billion in 2024.
Business email compromise alone accounted for about $3 billion. These are complaints people chose to file, so the real total is higher.
Security spending can offset part of that. IBM found that organizations using AI and automation extensively in security operations had breach costs $1.93 million lower and a lifecycle 65 days shorter.
2. Attackers use ordinary gaps, and the gaps are growing
In the 2026 DBIR, vulnerability exploitation was the initial access vector in 31% of breaches, overtaking stolen credentials (13%) for the first time in 19 years.
Defenders are moving the wrong way: only 26% of CISA’s known exploited vulnerabilities were fully remediated, down from 38%, and the median time to full patch rose to 43 days from 32.
Phishing remained the most common initial vector in IBM’s data for the fourth year in a row, followed by supply chain compromise (IBM 2026).
None of these routes is stopped by antivirus on its own. An unpatched edge device or a reused password sits outside what endpoint software covers.
3. Ransomware stops operations
Ransomware was involved in 48% of breaches in the 2026 DBIR, up from 44%. The encouraging part is that 69% of victims did not pay. That only works if you can restore without the attacker’s key, which means offline or immutable backups you have actually tested.
Disruption can cost a smaller business more than the ransom itself, as Help Net Security notes in its DBIR coverage. IBM’s 2025 edition measured extortion and ransomware incidents at $5.08 million on average when the attacker disclosed them.
A written recovery plan, with a named person for each step and a restore time you have measured, is what keeps a bad week from becoming a business-ending one.
4. Your suppliers are part of your attack surface
Third-party involvement in breaches rose 60% year-on-year to 48%. Only 23% of third-party organizations fully fixed their MFA issues, and for half of the weak-password and permission findings it took close to eight months to fix them.
Supply chain compromise was also IBM’s second most common initial vector.
The practical response is dull but effective: keep a list of every vendor with access to your systems or data, require MFA on those accounts, and remove access the day a contract ends.
5. People are still the way in
The human element was involved in 62% of breaches. The delivery channel is shifting: mobile social engineering, meaning fake texts and voice calls, succeeds 40% more often than email phishing.
IBM found vishing and smishing carried the highest average breach cost, $5.29 million, and listed help-desk impersonation and MFA fatigue among the top techniques.
Annual slide-deck training does little against that. Short, frequent exercises that include texts and phone calls, plus a clear rule that nobody resets a password or approves an MFA prompt on request, address how attacks actually arrive.
6. Customer trust and reputation
Lost business was one of the cost drivers IBM named behind the 2026 increase. The cost also reaches customers directly: in IBM’s 2025 edition, nearly half of breached organizations planned to raise prices afterward.
Customers hand you contact details, payment data and sometimes health or identity records. A visible breach tells them that trust was misplaced.
7. Regulation sets a legal floor
Which rules apply depends on where you operate and what data you hold. Two examples show the scale. Under the GDPR, the highest tier of fines reaches EUR 20 million or 4% of worldwide annual turnover, whichever is higher.
In the US, HIPAA civil penalties reach $73,011 per violation for most tiers and up to $2,190,294 for willful neglect left uncorrected, under the 2026 inflation-adjusted tiers.
Those are statutory maximums, and regulators weigh the size of the organization and the care it took. Having documented controls is what helps you in that weighing.
8. Intellectual property is a target
Trade secrets, product designs, source code and customer lists have value to competitors and to criminals who resell them.
Espionage-motivated breaches rely heavily on exploitation: the 2025 DBIR found vulnerability exploitation in 70% of them, compared with 20% across all breaches that year.
Protecting IP therefore comes back to the basics in reason 2: patching, access control, and knowing where your most valuable files live.
9. AI raises the stakes on both sides
Attackers use AI for deepfake impersonation, phishing and malware. IBM reported that more than one in four organizations hit by a malicious attack saw AI involved, a 56% increase that added about $1 million to the average breach cost.
The exposure is also internal: 92% of organizations with an AI-related security incident lacked adequate AI access controls, and the DBIR found employees using unapproved AI tools rose from 15% to 45% in a year. If staff paste customer data into a tool you have not vetted, that data has left your control.
Self-Assessment: Evaluating Your Organization’s Security Exposure
Only run these on accounts, devices and domains you own or administer.
- MFA audit: List every account that can reach email, admin consoles, payroll and remote access. Turn on MFA for each, using an authenticator app or security key rather than SMS where possible.
- Known exploited vulnerabilities: Open CISA’s Known Exploited Vulnerabilities catalog and check your routers, VPNs, firewalls and servers against it. Anything listed that you run gets patched first.
- Restore test: Pick one backup, restore it to a clean machine and time it. If you cannot, you do not yet have a backup you can rely on. Keep one copy offline or immutable.
- Breached credentials: Run a domain search on Have I Been Pwned for addresses at your company (you must verify domain ownership) and force resets for exposed accounts.
- Vendors and AI tools: Write down which suppliers have access to your systems and which AI tools staff use. Anything you cannot name is a gap.
FAQs
How much does a data breach cost a business?
IBM’s 2026 report puts the global average at $4.99 million and the US average at $11.5 million. These are averages across large and mid-sized breaches studied by IBM, so a small business will usually see a smaller absolute figure but a larger share of its revenue.
Do small businesses really get attacked?
Yes. In the 2025 DBIR, ransomware was present in 88% of breaches at small and medium businesses versus 39% at larger organizations. The equivalent split for the 2026 edition was not confirmed. Attackers go after whoever has weak, internet-facing systems, and size is not part of that filter.
Is antivirus and a firewall enough?
No. The most common routes in 2026 are exploited vulnerabilities, stolen credentials, phishing and compromised suppliers. Antivirus and a perimeter firewall address few of them. You also need patching, MFA, tested backups, staff awareness and control over vendor access.
What should a business do first?
Turn on MFA for email and admin accounts, patch anything on the known exploited list, and test a backup restore. Those three steps address the entry points and the recovery problem described above and cost little beyond staff time.
What does cybersecurity protect?
It protects customer and employee data, financial records, intellectual property, and the systems your business needs to operate. It also protects your ability to show customers and regulators that you handled that data responsibly.